I was tired of guessing at IP addresses, pinging them, and hoping nothing else was using them, so I wrote a scanner to do it properly. It runs 128 pings at once, reads the ARP cache at exactly the right moment to catch devices that don't answer pings, and figures out which network you're actually on instead of guessing. Here's how it works and the tricks that made it fast.
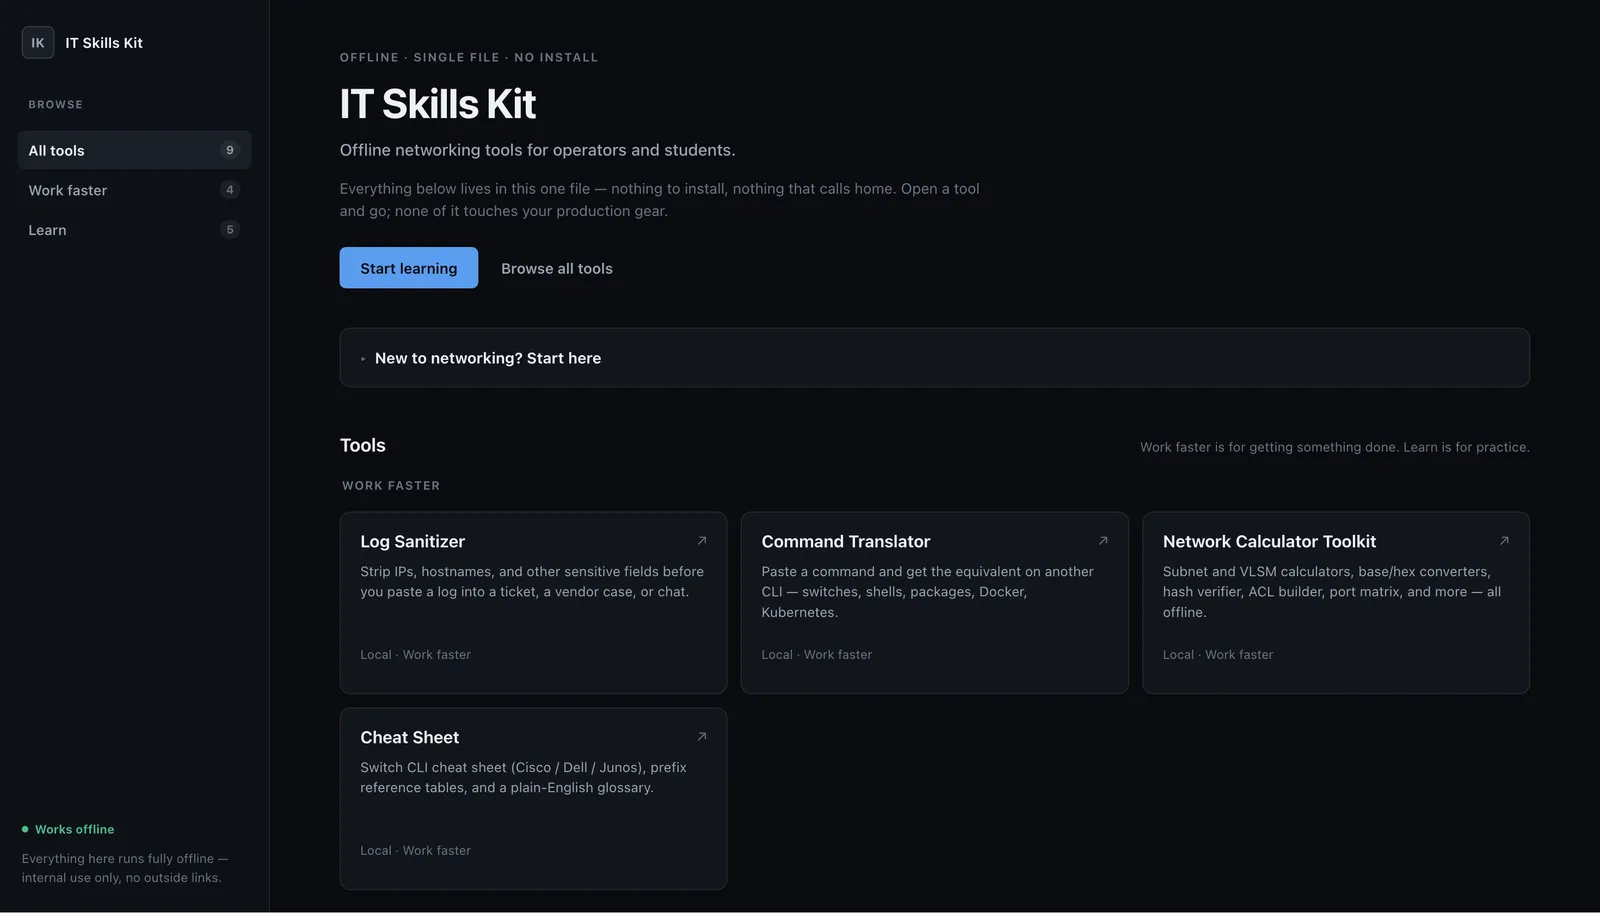
What started as one little tool for cleaning up logs before I pasted them somewhere kept growing. A CLI translator here, a subnet calculator there, then a handful of hands-on labs, and eventually it made more sense to stop pretending they were separate projects. Here's what's in the kit so far, and why I built each piece.
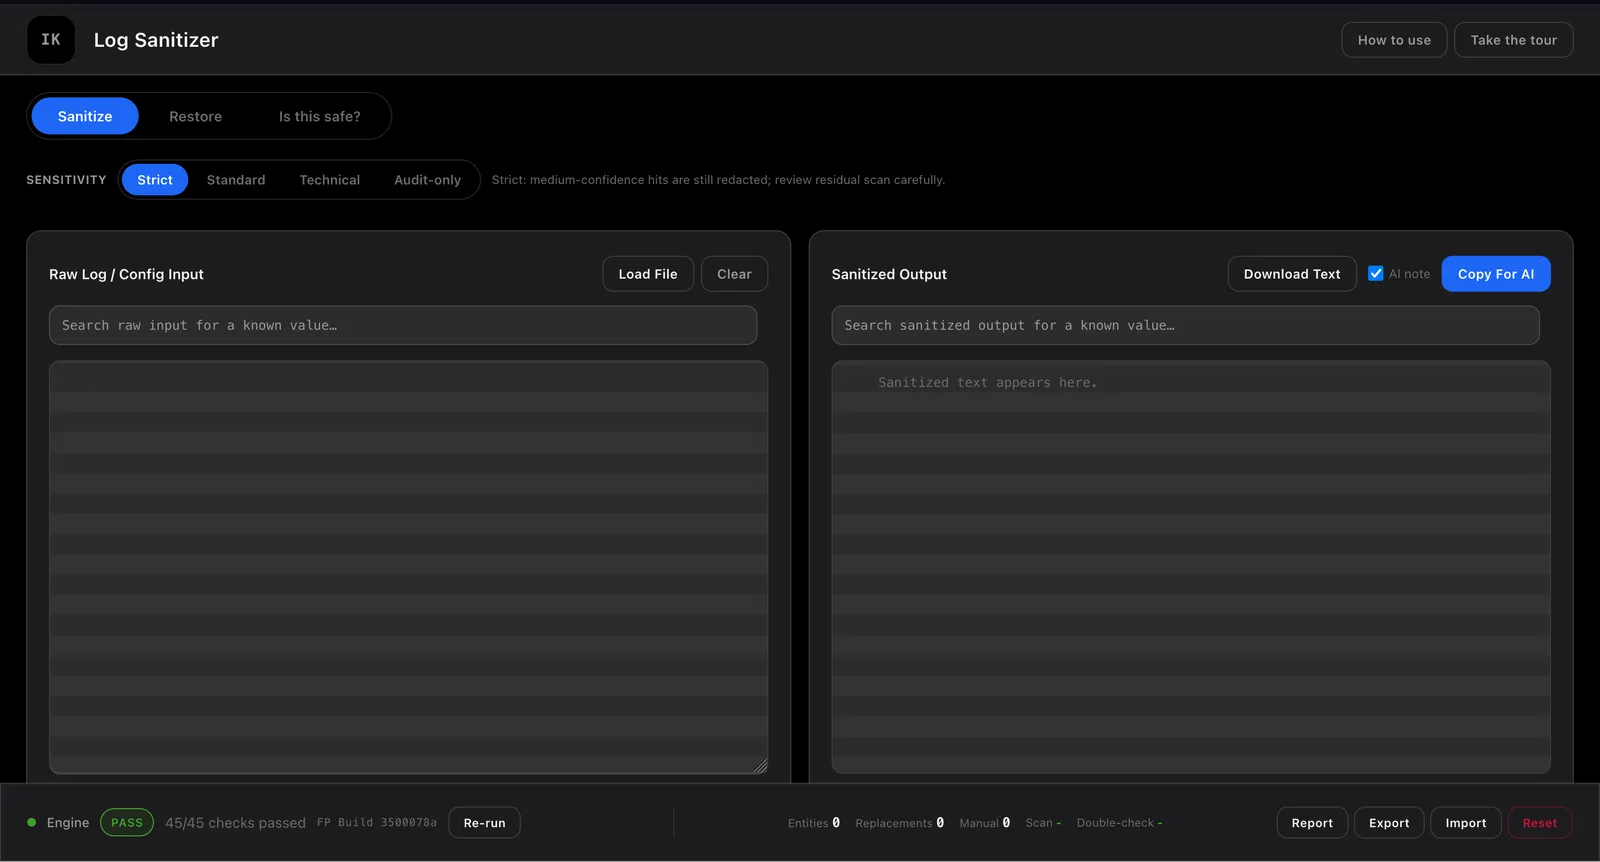
I kept running into the same problem: a log full of IPs, hostnames, and passwords that I needed to paste into a ticket or hand to an AI for help, and absolutely didn't want to hand-redact line by line. So I built a tool that does it for me, in real time, without any of it ever leaving my machine. Here's how it works, and why I still reach for it more than anything else in the kit.